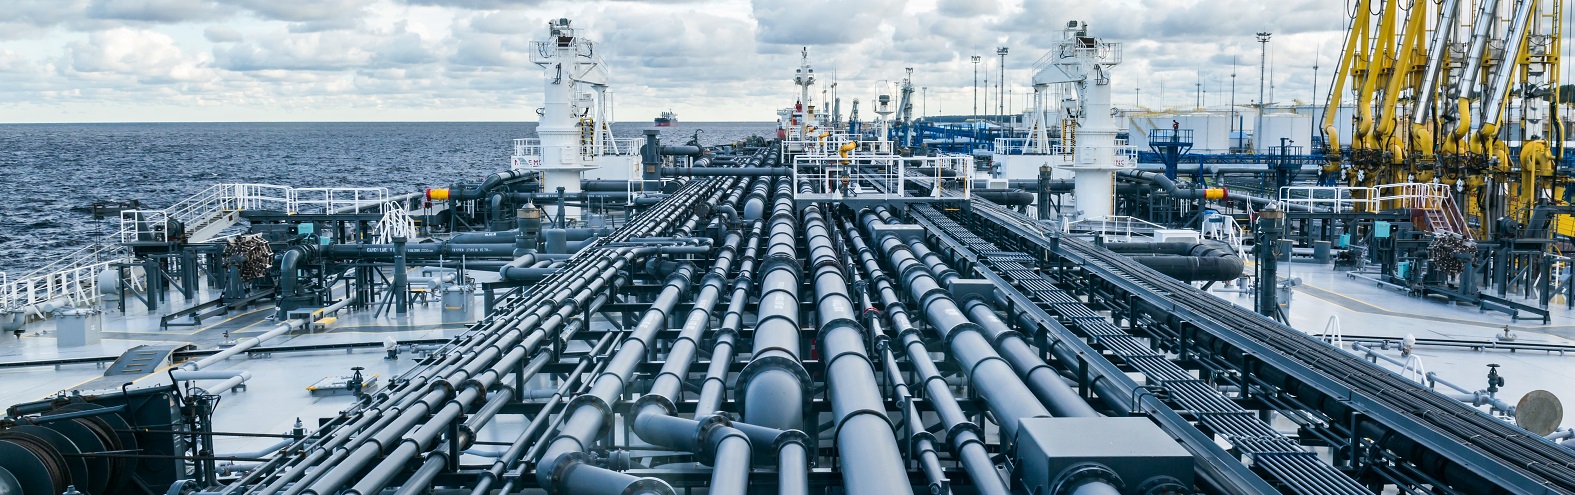
No one wants to repeat the week-long Colonial Pipeline shutdown, or—even worse—see a critical infrastructure cyber attack that manages to infiltrate a pipeline’s operational technology network and cause physical damage. In the aftermath of the Colonial ransomware attack, oil and gas pipeline operators, terminal management system providers, and federal regulators are all taking a close look at pipeline cybersecurity standards and practices.
The pipeline industry—at least for now—lacks an equivalent to the North American Electric Reliability Corporation (NERC), which sets cybersecurity requirements for power generation, transmission, and distribution companies. Even so, some pipeline operators (including Owl Cyber Defense customers) already have robust, multi-level cyber defenses in place. The rest of the industry will need to catch up quickly to comply with the Department of Homeland Security’s new pipeline security directive, which mandates new cybersecurity assessments and mitigation plans for the country’s largest pipelines.
Which leads us to the question: what needs to change to prevent a repeat of the Colonial Pipeline shutdown?
There’s no single answer to that question. There were multiple issues with Colonial’s cyber defenses that permitted the successful attack. But the biggest problem was Colonial’s uncertainty as to whether the attack had penetrated to the OT systems that physically control pipeline operations. Without assurance that its OT systems were secure, Colonial had no choice but to shut down. And so, a ransomware attack that might have been a minor inconvenience became a national disruption.
The key to secure, resilient pipeline infrastructure is maintaining rigorous segmentation between enterprise IT networks and OT networks. If operational technology doesn’t need to be connected to external networks, it should be completely isolated. But when (as is usually the case) OT systems need to be connected to IT networks for monitoring, command and control, software patching, or other purposes, the connections should be as tightly controlled as possible.
Owl Cyber Defense solutions have been trusted by pipeline operators and other critical infrastructure customers for more than 20 years. Owl’s hardware-enforced security solutions provide one-way data transfer, segmented two-way transfer, data filtering, and other capabilities that allow operators to transfer OT data while minimizing cyber threats, even when an organization’s IT systems have been compromised.
To learn more about how Owl Cyber Defense is helping pipeline operators protect their critical systems, contact us for a consultation today.